Can Finance Teams Set Merchant Locks on Corporate Cards?
Merchant locks can restrict corporate card use by category or named merchant. Learn how each control works, where it can fail and what finance teams should verify before rollout.
Finance teams can set merchant restrictions on corporate cards when their card provider supports them. Merchant category code controls allow or block broad categories, while named-merchant locks restrict spending to or from a specific business. Because merchant identifiers and category codes are assigned through payment processing, neither control is perfect. Finance teams should verify enforcement scope, update timing, permissions, exception handling and audit records before relying on a merchant lock.

What does a merchant lock do?
A merchant lock controls where a corporate card can be used. Depending on the card programme, finance teams may be able to block selected merchant categories, allow only approved categories, prohibit a named merchant or create a card that works only with a particular merchant.
These capabilities are often grouped under the label merchant controls, but they are not interchangeable. A merchant category restriction evaluates the merchant category code, or MCC, submitted with the transaction. A named-merchant restriction evaluates merchant information such as an identifier or descriptor. A spend limit controls the amount rather than the merchant.
The distinction matters because a platform that advertises merchant controls may support MCC rules without supporting named-merchant locks. Finance teams should ask which transaction fields are evaluated and whether the rule is an allowlist, a blocklist or both.
Merchant locks versus other card controls
| Control | What it evaluates | Best use | Main limitation |
|---|---|---|---|
| MCC block | The merchant category code submitted with the authorisation | Blocking categories such as gambling, cash withdrawals or entertainment | The processor-assigned category may not reflect the item purchased |
| MCC allowlist | Whether the submitted MCC appears on an approved list | Restricting a travel card to airlines, hotels and transport | Unexpected merchant classification can cause legitimate declines |
| Named-merchant allowlist | Merchant identifiers or descriptors available to the card programme | Creating a card for one software vendor or advertising platform | Identifiers can vary by region, branch, payment facilitator or processor |
| Named-merchant block | Merchant information associated with a prohibited business | Preventing purchases from a known merchant | A differently presented merchant identity may not match the rule |
| Spend limit | Transaction or cumulative amount | Setting a per-purchase, daily or monthly budget | Controls how much can be spent, not where |
| Card freeze | Whether the card is active | Responding to loss, suspected misuse or employee departure | Previously authorised transactions and some adjustments may still settle |
How merchant restrictions work during authorisation
An MCC is a four-digit code used to classify a merchant by its primary business activity. The merchant’s acquiring side supplies this classification as the payment travels through the card network. The code describes the merchant, not the individual product or service being purchased.
When an employee uses a corporate card, the authorisation request generally contains the amount, currency, merchant information, MCC and transaction characteristics. The card programme can evaluate those details alongside the active controls:
- Is the card active?
- Is the merchant or merchant category permitted?
- Does the amount fit within the applicable transaction and cumulative limits?
- Is the transaction type, such as an ATM withdrawal, allowed?
- Is sufficient funding available for the authorisation?
If the request breaches a control, it can be declined during authorisation rather than approved and flagged afterward. However, finance teams should not assume every policy change reaches the authorisation system instantly. They should confirm how quickly updates take effect and how the programme treats transactions that were authorised before a rule changed.
Why named-merchant locks require careful testing
A named merchant is not always represented by one consistent label. A business may process transactions through different legal entities, regional accounts, branches or payment facilitators. The descriptor shown on a card statement may also differ from the identifier used to evaluate a restriction.
This means a card intended for one supplier can decline a valid charge if that supplier changes its processing setup. The reverse problem is also possible: a broad or inconsistent matching rule may permit transactions that finance expected to block.
Before depending on a named-merchant lock, ask what field is matched, whether multiple merchant identities can be added and how card-on-file transactions are handled. A low-limit test card and a real transaction provide better evidence than a dashboard label alone.
Should controls apply per card or per employee?
Card controls are commonly attached to an individual card credential, even when a platform presents policies by employee, team or department. Per-card enforcement allows one employee to have different rules for different purposes. For example, a virtual card could be reserved for software subscriptions while a physical travel card permits airlines, hotels and ground transport.
Group policies are easier to administer across many cardholders, while card-specific rules provide tighter budgeting and separation of purposes. A practical design often combines a standard departmental policy with narrower limits or exceptions on individual cards.
Finance teams should verify:
- Whether changing an employee or team policy updates every associated card.
- Whether one cardholder can have cards with different merchant rules.
- Whether replacement cards inherit the previous controls.
- Whether virtual, physical and wallet-tokenised cards follow the same rules.
- Whether policies can be reviewed by legal entity, department or cost centre.
Permissions and separation of duties
Individual cardholders should not be able to remove the restrictions governing their own cards. Configuration should be limited to authorised finance or treasury users, with higher-risk changes subject to review where the platform and company process permit it.
A workable division of responsibilities is:
- Administrators: issue cards and configure approved controls.
- Approvers: review high-value limits, new card requests and exceptions.
- Cardholders: use cards and submit supporting documentation without changing policy.
- Reviewers: inspect transactions, control changes and reconciliation evidence without issuing cards.
Confirm the actual roles available rather than assuming the interface supports this exact structure. For audit purposes, control changes should be attributable to a user and time, with the previous and new settings retained or otherwise exportable. Finance should also document approvals outside the card platform if its role or audit capabilities are insufficient.
How to manage legitimate exceptions
Merchant restrictions can create valid declines. A hotel may process an ancillary service under another MCC, while a marketplace may use its own category instead of the category of the underlying goods. The exception process should resolve the purchase without permanently weakening the policy.
- Temporarily permit the required category, then restore the restriction.
- Issue a separate virtual card with a fixed limit and narrow purpose.
- Use another approved payment method when the transaction cannot fit the card policy.
- Require approval before an administrator changes a merchant rule or limit.
- Record the business purpose, approver, owner and required reversal time.
If the platform cannot expire a temporary change automatically, assign someone to reverse it and verify completion. Repeated exceptions should trigger a policy review, but they should not automatically result in a permanently unrestricted card.
Where merchant controls can fall short
MCC controls govern merchant classification, not the contents of a basket. An approved office-supply merchant may also sell gift cards or consumer electronics. Merchant restrictions therefore complement rather than replace receipt collection, transaction review, accounting coding and reconciliation.
Finance teams should test or obtain clear answers for these transaction patterns:
- Online marketplaces and payment facilitators.
- Recurring subscriptions and card-on-file charges.
- Mobile wallets and tokenised card credentials.
- Hotel, fuel and car-rental pre-authorisations.
- Tips and adjustments that differ from the original authorised amount.
- Refunds, reversals and transactions presented after a delay.
- Merchants operating under regional entities or varying descriptors.
Pre-authorisations deserve particular attention. A hotel or car-rental company may authorise an estimated amount before the final charge is known. Changing or freezing the card afterward does not necessarily erase an authorisation that has already been granted, and the final settlement amount can differ from the initial request.
Provider due-diligence checklist
- Define the required control. Decide whether the use case needs an MCC block, MCC allowlist, named-merchant rule, amount limit or a combination.
- Confirm enforcement scope. Ask whether rules apply per card, cardholder, team, legal entity or card programme.
- Check update timing. Determine when new rules and changed limits reach authorisation decisions.
- Inspect permissions. Identify who can issue cards, modify controls, freeze cards and approve exceptions.
- Review decline information. Confirm whether finance can distinguish an MCC decline from a limit, funding or card-status failure.
- Verify audit evidence. Check whether card issuance, policy changes, approvals and transactions can be exported for reconciliation and audit support.
- Run controlled tests. Use low limits to test expected approvals, expected declines, recurring charges and pre-authorisations before broad rollout.
Applying the controls in a treasury environment
Start with the narrowest policy that still supports the card’s business purpose. Separate cards by use case, set limits consistent with expected spend and establish an exception owner before distribution. Review early declines to identify valid merchants with unexpected classifications.
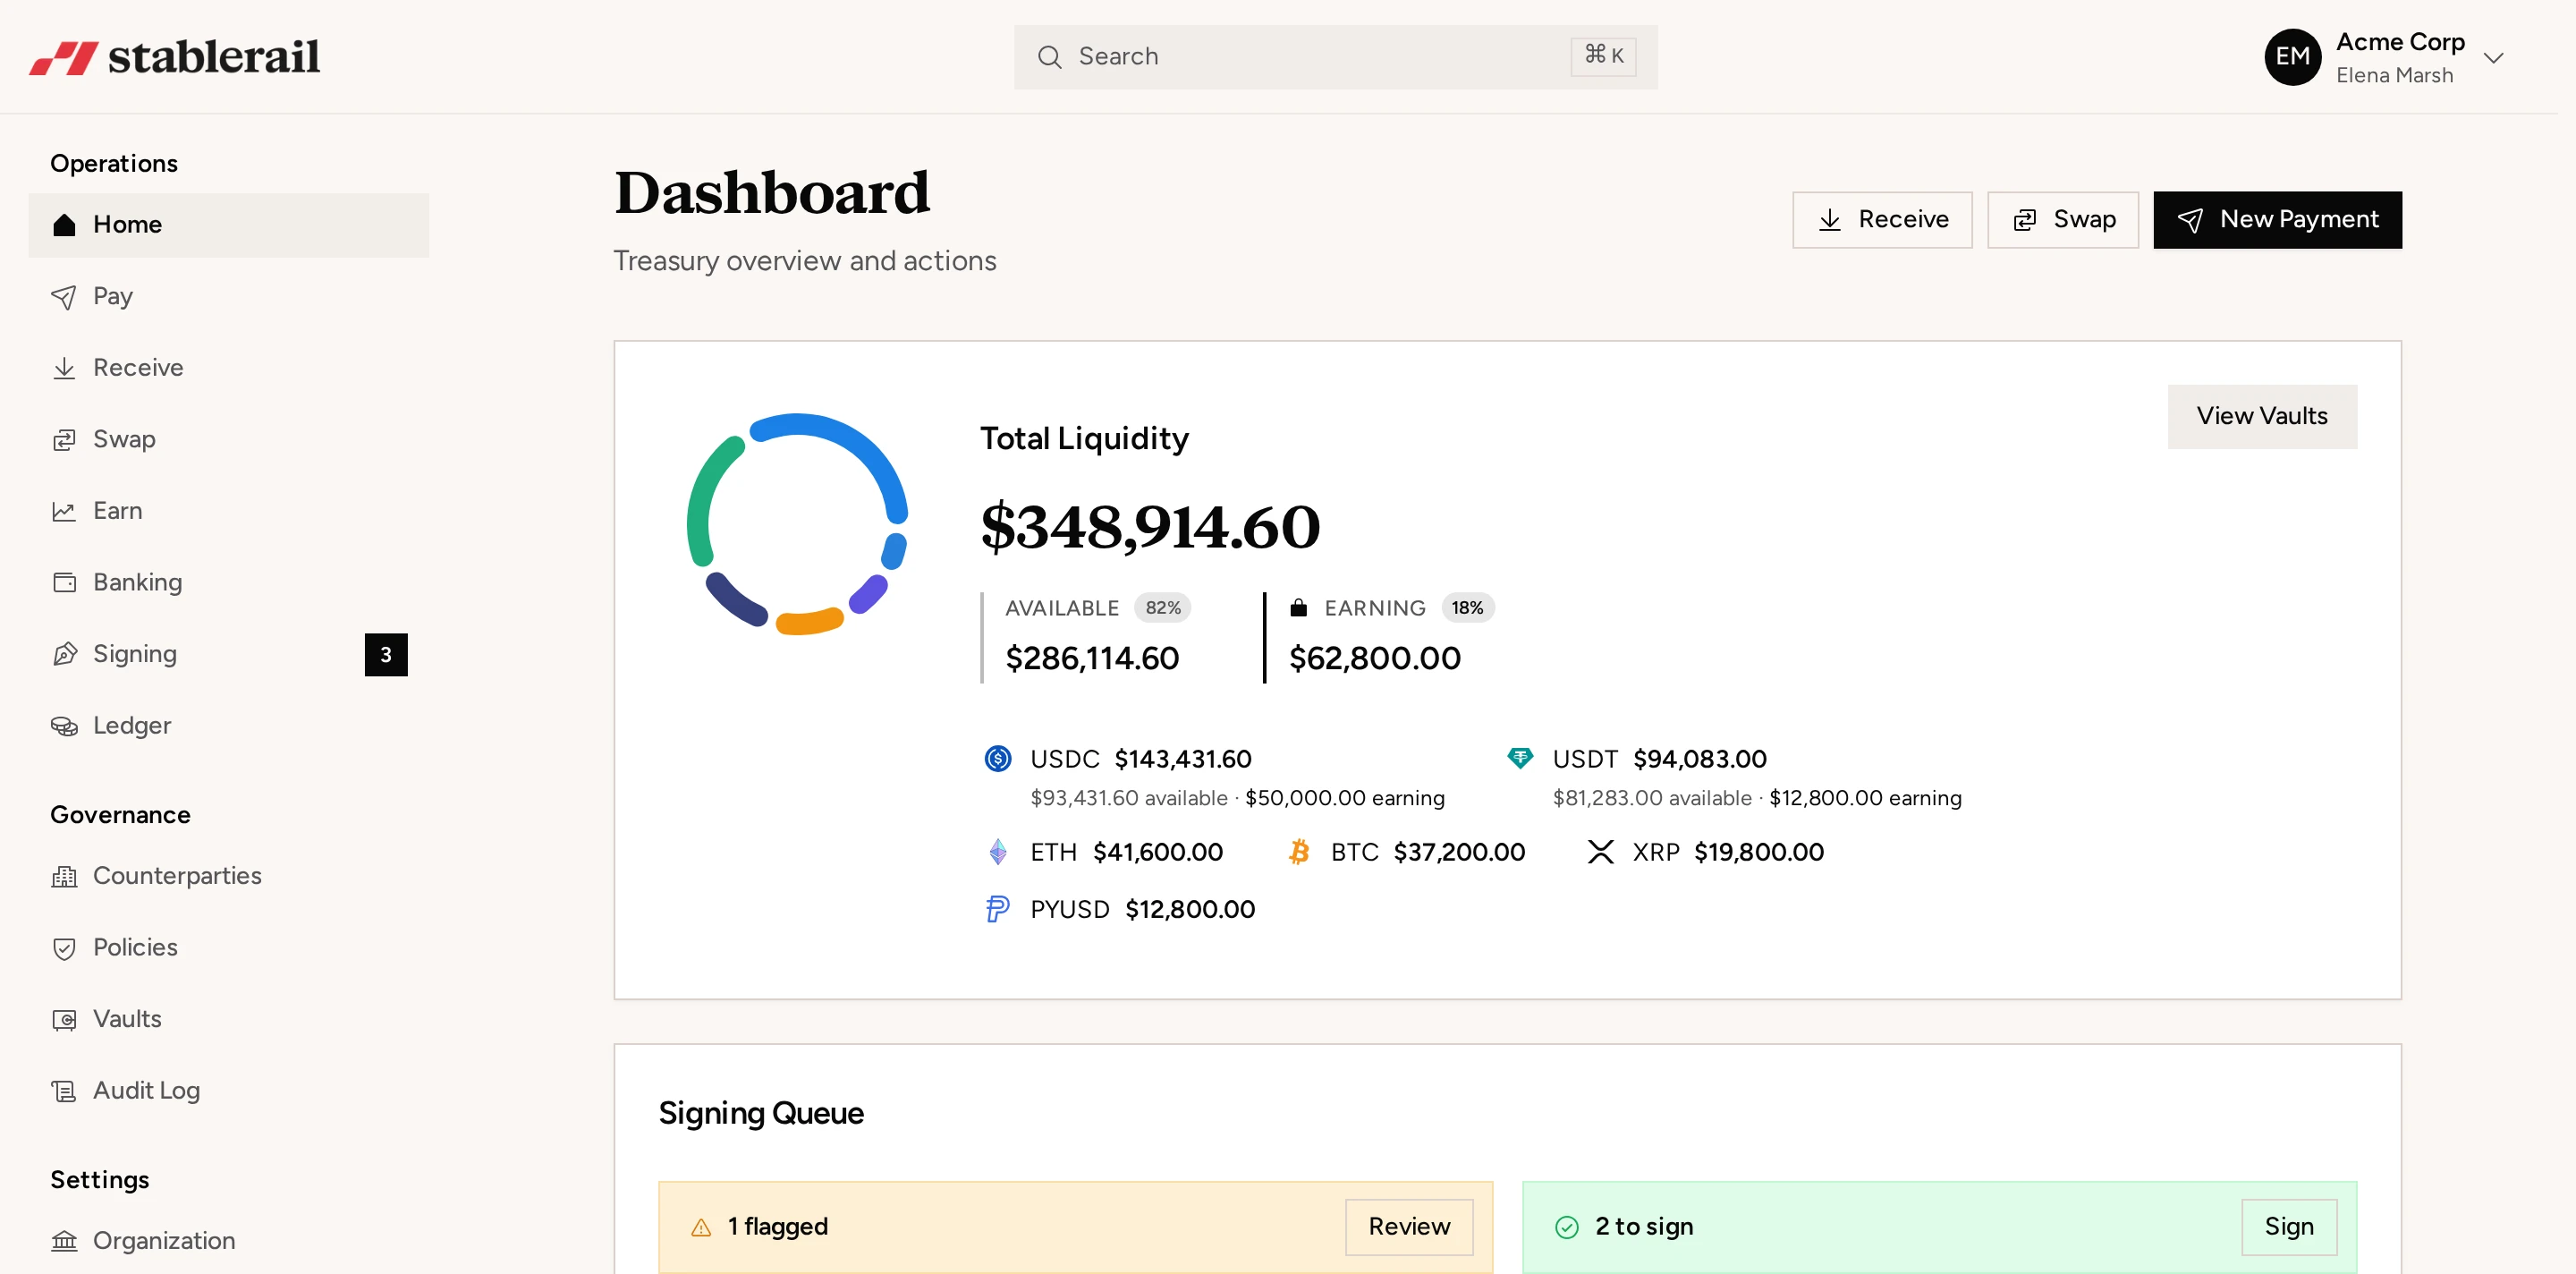
Stablerail provides corporate cards funded from the company’s own treasury balance, with card limits and MCC controls alongside approvals, signing quorum, global payouts, fiat conversion and exportable audit evidence. The exact card configuration can depend on the company and card programme, so a team that requires named-merchant restrictions should confirm that specific capability during onboarding rather than treating MCC controls as equivalent.
The decisive question is not whether a provider advertises spend controls. It is whether the available restriction evaluates the right merchant data, applies at the required level and produces reliable evidence when a payment is approved, declined or changed.
Frequently asked questions
Can a corporate card be locked to one merchant?
Yes, if the card provider supports named-merchant allowlists. Confirm how the merchant is identified because descriptors and identifiers may vary by legal entity, region, branch or payment processor.
What is the difference between a merchant lock and an MCC restriction?
A named-merchant lock targets a specific business using available merchant identifiers. An MCC restriction permits or blocks a category of businesses, such as hotels or advertising services, based on the category code submitted with the transaction.
Can MCC controls prevent employees from buying specific products?
No. An MCC describes the merchant’s primary business category, not each item in the purchase. Receipt collection, transaction review and reconciliation are still needed to determine what was bought.
Why was an approved merchant declined on a corporate card?
The merchant may have submitted an unexpected MCC or processed the charge through a different entity or payment facilitator. Other possible causes include a spend limit, insufficient funding, a frozen card or a transaction type that the card does not permit.
Do new merchant restrictions take effect immediately?
That depends on the provider and card programme. Finance teams should ask when policy updates reach the authorisation system and whether existing pre-authorisations or previously approved recurring transactions are affected.
Finance writers covering stablecoin treasury, payments, compliance, and risk controls.
More about the Stablerail team- Stablecoin treasury managementApprovals, limits, yield and reporting on one balance.
- Stablecoin payoutsBatch contractor and vendor payments with screening.
- USDT vs USDCWhich stablecoin your company should settle in.
- Stablecoin finance glossaryMPC, off-ramp, travel rule and the rest, in plain English.
- Product updatesEverything we ship, month by month.